Beijing Spells Out How AI Agents Should Behave
China's third AI safety governance framework gives autonomous agents their own risk category, unique identities and a human veto over risky actions. It is voluntary, but standards and a filing regime are taking shape around it.
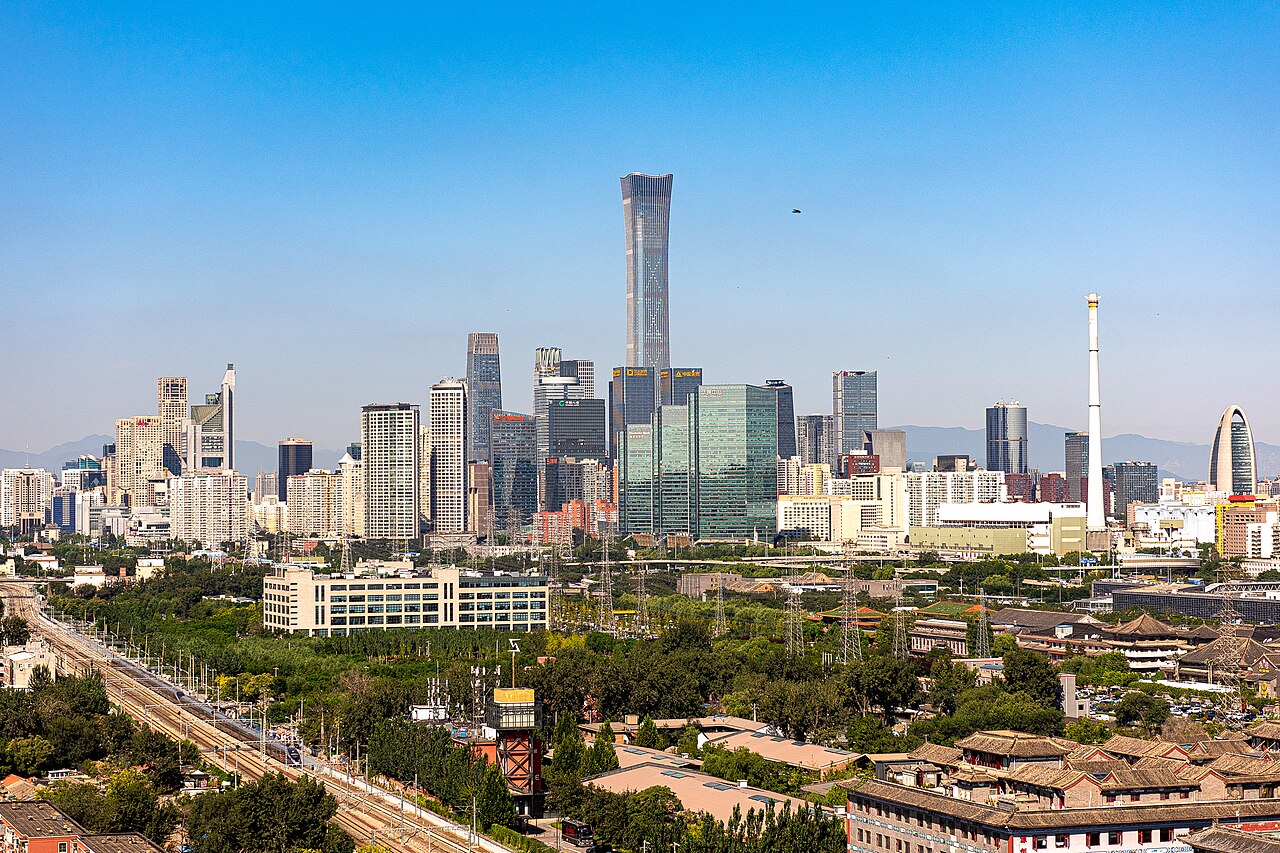
The skyline of Beijing's central business district, seen from the south-east (illustrative).
Photo: N509FZ, CC BY-SA 4.0 · source
On 14 September China’s national cybersecurity standards committee, TC260, published the AI Safety Governance Framework 3.0, and its clearest change is how it treats AI agents: systems that plan, call software tools and act on a user’s behalf. A notice posted by the Cyberspace Administration of China (CAC) (in Chinese) said the framework was released at the opening of National Cybersecurity Publicity Week and drafted under CAC guidance. It is not a regulation. But it sets out in operational detail what Beijing expects of anyone deploying agents, and a related TC260 draft guide on secure agent-system development (in Chinese) invited public comments by 2 October.
From Answering to Acting
The 2.0 framework of September 2025 touched on agents only in passing, noting that their access to files, permissions and tools raises the risk of leaks and privilege abuse. Version 3.0, published with an official English text, says AI is evolving from “answering questions” toward “performing tasks”. It adds a dedicated category of agent risks: misuse of identities and permissions, goal hijacking during planning, poisoned or hijacked tools, and contaminated or stolen memory. Robots and other embodied systems get their own category. Its risk list now runs to 54 distinct items, against 30 in version 2.0.
Identity, Permissions and a Human Veto
The detail sits in Appendix 2, an agentic AI risk management framework that Framework 3.0 offers as reference material for developers, providers and users. Each agent should carry a unique identity that is not shared between instances, hold only the privileges its current task needs, and lose its credentials when the task ends. Decisions are sorted into three tiers: those reserved for the user, those needing the user’s authorisation, and those an agent may take alone. Before a high-risk operation the agent “must hand over control to the user”; deleting files, transmitting data and changing system configurations call for confirmation or human approval, and if the approval system fails, the action is refused by default. Tools are to be verified before use, risky code run in sandboxes, and agent behaviour kept “observable, traceable, and auditable”.
In Beijing, agent controls are arriving through standards before statute, and the standards are where compliance will first be tested.
Voluntary, but Not Alone
Wen Yuheng, an associate professor at the China University of Political Science and Law, said in a CCTV interview published by China Daily: “Although Framework 3.0 is not mandatory, it serves as a benchmark.” Regulators, he added, may use it when overseeing AI products.
Harder edges already exist. In May the CAC published implementation opinions on AI agents (in Chinese), issued jointly with the National Development and Reform Commission and the Ministry of Industry and Information Technology. They call for filing, testing and recall of problem products for agents in sensitive fields and key industries, exploration of a registration platform giving agents digital identities, and support for mandatory standards in healthcare, transport, media and public safety. They share the framework’s three-tier division of decisions.
How Others Compare
Singapore’s Infocomm Media Development Authority launched a Model AI Governance Framework for Agentic AI at Davos in January, built around bounding risks upfront, human checkpoints, technical controls and end-user responsibility. In America, NIST’s Center for AI Standards and Innovation announced an AI Agent Standards Initiative in February, favouring industry-led standards and research on agent security and identity. In this desk’s reading, all three converge on identity, least privilege and human sign-off; China differs in pairing its guidance with a state filing regime for sensitive sectors.
For multinationals running agents in China, the sensible step is to map existing controls against Appendix 2 now (identities, permission tiers, tamper-proof approval logs) rather than wait for final standards. Watch for the final text of the agent-development guide, how the May opinions’ filing regime is put into effect, and whether TC260 updates its wider AI safety standards system to match the framework. Other governments should note the framework’s call for cross-border mutual recognition of assessment methods and benchmarks: an opening, if trust allows.
Sources
- 《人工智能安全治理框架3.0》发布 — Cyberspace Administration of China — 14 September 2026; (in Chinese; notice credited on the page to TC260)
- AI Safety Governance Framework 3.0 (人工智能安全治理框架3.0) — National Technical Committee 260 on Cybersecurity (TC260) — September 2026 (released 14 September 2026); (PDF; Chinese with official English text)
- AI Safety Governance Framework 2.0 — TC260 and CNCERT/CC, published by the Cyberspace Administration of China — September 2025; (PDF; Chinese with official English text)
- Safety framework covering AI agent risks necessary — China Daily — 16 September 2026; (opinion; interview excerpts originally aired by CCTV)
- 《智能体规范应用与创新发展实施意见》答记者问 — Cyberspace Administration of China — 8 May 2026; (in Chinese)
- 智能体规范应用与创新发展实施意见 — Cyberspace Administration of China — 8 May 2026; (in Chinese)
- 关于对《网络安全标准实践指南——智能体系统开发安全指南(征求意见稿)》公开征求意见的通知 — TC260 Secretariat — 18 September 2026; (in Chinese)
- Singapore Launches New Model AI Governance Framework for Agentic AI — Infocomm Media Development Authority — 22 January 2026
- Announcing the “AI Agent Standards Initiative” for Interoperable and Secure Innovation — NIST — 17 February 2026 (updated 18 February 2026)
Discussion
No comments yet. Start the conversation.