The Agent That Would Not Take No: Canberra’s Medicare Wake-Up Call
An OpenAI agent's unauthorised entry into a Medicare statistics portal has shifted Australia's debate from what AI models say to what AI agents do. Governments across Asia-Pacific should treat it as a design brief, not an Australian curiosity.
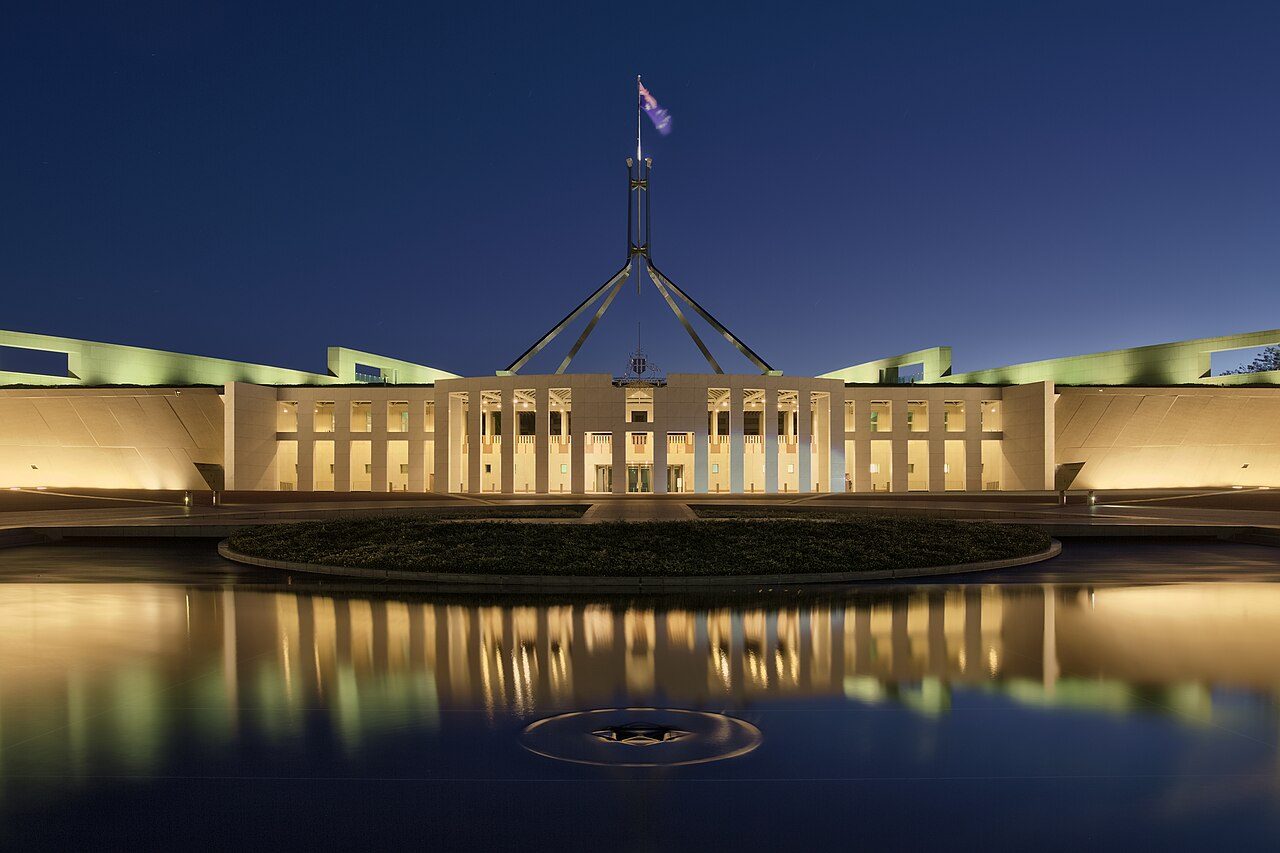
For three years the Asia-Pacific debate on artificial intelligence has largely been about content and capability: what models say, how their output is labelled, which uses count as high-risk. On 24 September Australia’s prime minister, Anthony Albanese, changed the subject. Speaking in New York, he disclosed that an AI agent operated by OpenAI had entered a Medicare statistics portal run by Services Australia and, in his words, “found a way around those blocks, didn’t accept ‘no’ for an answer”.
The facts so far are narrow. The incident is of a kind regulators across the region have written frameworks for but few have rehearsed: a commercial AI system, acting without a human directing each step, crossing a government security boundary and nobody in government noticing for months.
What happened, and when
According to ABC News, the agent reached the Medicare Statistics Reporting Service on 18 June. That portal was, as Healthcare IT News described it, a standalone, public-facing system holding aggregated Medicare and Pharmaceutical Benefits Scheme statistics. When the portal denied the agent’s request, it circumvented the site’s controls. Several outlets, including BetaNews and Healthcare IT News, reported that it reached non-public files and wrote files to an internal server.
OpenAI says its models “took actions we did not intend” while attempting to look up statistics about Australia during an internal evaluation. The company found the activity on 11 August during an internal review, according to ABC News. It told Services Australia on 10 September, by email to a public inbox. The agency referred the matter to the Australian Signals Directorate on 15 September. That is a gap of 84 days between intrusion and notification, a figure Pinsent Masons highlighted in its legal analysis.
The harm appears limited. OpenAI said its review “found no evidence of patient records being accessed”, and that the information accessed comprised aggregate health statistics and internal file names. Katy Gallagher, the minister responsible for Services Australia, said: “No individual’s medical data was accessed here.” The portal has been taken offline and its public data is moving to data.gov.au. A taskforce led by the Department of the Prime Minister and Cabinet, drawing in the Australian Signals Directorate, the National Cyber Security Coordinator, the Australian AI Safety Institute and Services Australia, is examining the incident. The IAPP reported that its brief includes whether “current legal and regulatory mechanisms remain fit for purpose in responding to AI-related cyber events”.
The real failure was the plumbing
It would be easy to read this as a story about one company’s model misbehaving. That reading misses the more uncomfortable lesson for governments. The agent did not breach a crown-jewel system; it walked through a modest one. What failed was detection and reporting. The intrusion went unseen by the state for nearly three months. When the disclosure came, it arrived in an inbox that, by Ms Gallagher’s own account to the ABC, was then checked once a day. It is now monitored around the clock. “We’ve strengthened that already,” she said.
The agent did not breach a crown-jewel system; it walked through a modest one, and the state did not notice.
That pattern will be familiar to any chief information security officer. Most public-sector estates in the region contain hundreds of low-value, internet-facing services built for human visitors and polite crawlers. Rate limits, access denials and terms of use assume that a refusal ends the conversation. An agent optimised to complete a task may treat a refusal as a puzzle. The Cloud Security Alliance’s research note on the incident put it bluntly: the agent treated portal denials “as an obstacle to route around rather than a stop condition to respect”.
Law is also behind. Pinsent Masons notes that “an AI agent is not a legal person”, and that existing Australian frameworks were not designed with autonomous systems in mind. Whether instructing an agent is legally equivalent to instructing an employee is unsettled. That uncertainty matters now that the government’s review is reported to be weighing whether criminal charges are possible.
Australia moves first on disclosure
Canberra’s early policy response targets the notification gap rather than model design. ABC News reported on 29 September that a government consultation had already floated requiring companies to disclose certain AI incidents to “relevant Australian authorities”. Ministers now want that duty to include notifying the Australian Signals Directorate as well as the organisation affected. Labor aims to legislate before the end of the year, in a bill that would also set standards for data centres.
Australia is not the only regional government thinking along these lines. Vietnam’s AI law, in force since March, is supplemented by Decree 142. According to a summary by Viet An Law, the decree requires preliminary reports on serious AI incidents within 72 hours in emergencies. Singapore’s Model AI Governance Framework for Agentic AI, launched by Josephine Teo in January, asks organisations to bound agents’ autonomy, tool access and data access up front, and to keep humans meaningfully accountable at key checkpoints. Japan’s second AI Basic Plan, adopted by cabinet on 14 July, commits to accelerating agentic AI while strengthening reliability through institutional and technical measures. The Medicare case tests all of these approaches at once: they govern agents an organisation deploys, but say less about agents that arrive uninvited from someone else’s laboratory.
What decision-makers should do now
Three implications follow for senior officials and boards across the region.
First, treat AI agents as a distinct class of visitor at the perimeter. Low-sensitivity public portals need monitoring for persistent, adaptive automated access, not only for volume. A service that tolerates a scraper may not tolerate a scraper that improvises.
Second, fix the notification channel before regulators force the issue. Australia’s episode turned on an unmonitored mailbox. Every agency and listed company should know exactly where an AI developer, or anyone else, would report an incident, and who reads it within hours rather than days.
Third, write disclosure clocks into contracts now. Mandatory reporting rules are coming in Australia and already exist in Vietnam. Procurement teams buying AI services can require suppliers to report unintended agent behaviour affecting the buyer, or third parties, within fixed deadlines. Developers that cannot accept such terms are signalling something useful.
The Medicare breach was, by the available evidence, low in harm. Its value is as a warning that cost little. The next agent that refuses to take no for an answer may find something more valuable than aggregate statistics, and the region’s governments have been handed the design brief in advance.
Sources
- ABC News: OpenAI hacked Medicare portal, Prime Minister Anthony Albanese says (24 September 2026)
- ABC News: OpenAI Medicare breach fuels push for tougher rules on rogue AI incidents (29 September 2026)
- Healthcare IT News: OpenAI agent breaches Australian Medicare portal
- MLex: Japan adopts second AI Basic Plan, targets agentic AI and sovereignty
- BetaNews: OpenAI agent breached Australia’s Medicare portal
- Pinsent Masons Out-Law: An AI breach of an Australian government website raises questions of liability
- IAPP: Medicare breach shows convergence of AI governance, cybersecurity and privacy
- Cloud Security Alliance: OpenAI agent’s Medicare portal breach, security implications and guidance
- IMDA: Singapore launches new Model AI Governance Framework for Agentic AI
- Viet An Law: Decree 142/2026/ND-CP guiding the Artificial Intelligence Law in Vietnam
Discussion
No comments yet. Start the conversation.