Peru Names an AI Officer in Every Ministry
Lima has named an owner for AI in every public body, with staggered deadlines and a profile that bites in a year. Santiago, meanwhile, is delaying the data-protection law that stands up the regulator any AI law would rely on.
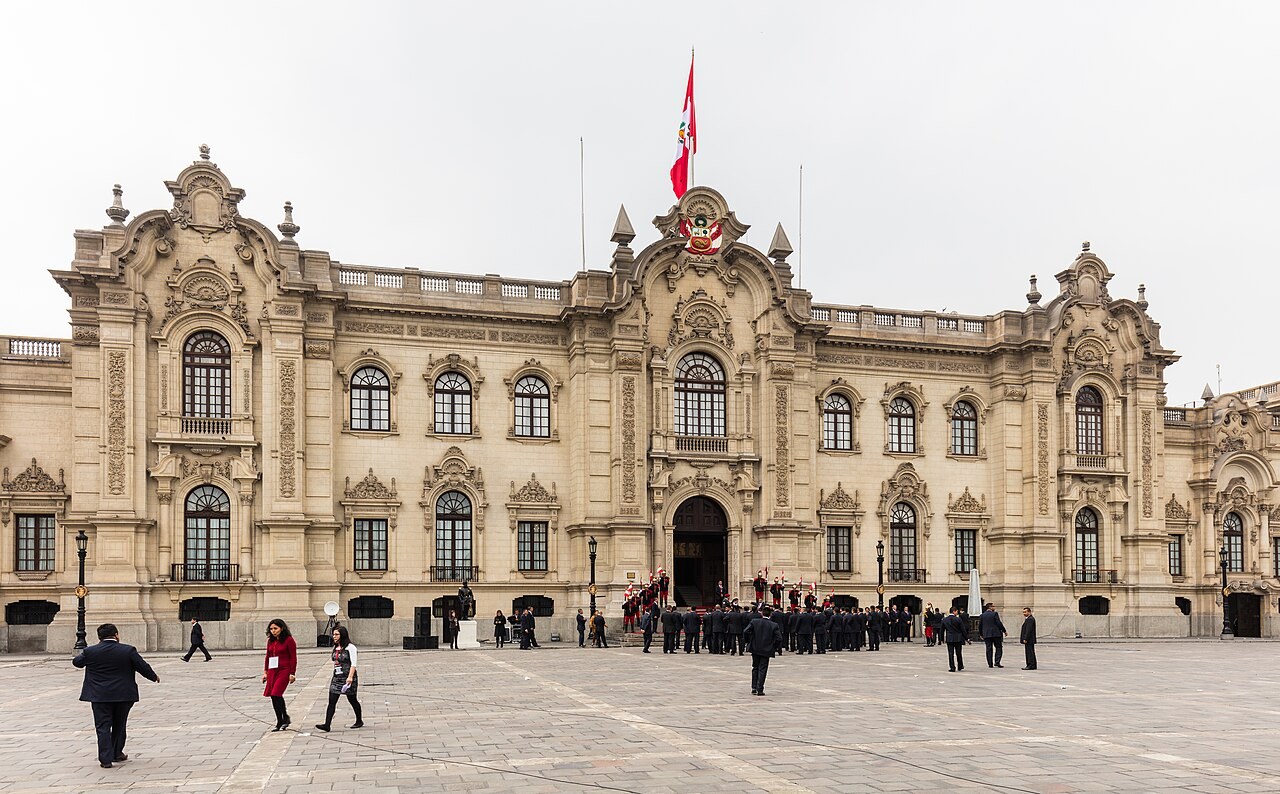
The Palacio de Gobierno in Lima, seat of Peru’s executive; the new directive on the Oficial de Inteligencia Artificial was issued by the Presidencia del Consejo de Ministros. Illustrative.
Photo: Diego Delso, CC BY-SA 4.0 · source
Peru has given artificial intelligence a named owner in every public body. Resolución de Secretaría de Gobierno y Transformación Digital N° 004-2026-PCM/SGTD, signed on 19 October 2026 and published in the gazette El Peruano on 21 October, approves Directiva N° 002-2026-PCM/SGTD, setting the profile, appointment criteria and duties of an Oficial de Inteligencia Artificial (OIA). It took effect on 22 October 2026. On 20 October a Chilean Senate committee moved the other way, advancing a bill that postpones the data-protection law creating the regulator any Chilean AI law would lean on.
What Lima has created, and who has to fill it
The OIA is a role rather than a new payroll line. The directive lets it be added to an official’s existing functions, requires no budgeted post, and seats the appointee on the entity’s Comité de Gobierno y Transformación Digital (CGTD) with voice and vote. The senior administrative authority appoints by resolution. The holder has technical autonomy and may not be removed or sanctioned for the content of technical opinions. Prime Minister Luis Galarreta called the directive “un hito más hacia la modernización del Estado” — another milestone in modernising the state — in El Peruano.
The duties are operational, not advisory. The OIA writes the institutional policy on safe, responsible and ethical AI use; formulates and directs the entity’s Plan de Acción de Inteligencia Artificial, and must see it folded into the Plan de Gobierno Digital; reports monthly to the top authority and quarterly to the CGTD; coordinates risk categorisation and impact assessment with the data-protection and digital-security officers; oversees the institutional register of its AI systems; and must ensure validation tests precede deployment. Each system’s cost, support included, is reviewed quarterly.
| Instrument | What it creates | Who is bound | The clock |
|---|---|---|---|
| Resolución SGTD N° 004-2026-PCM/SGTD and Directiva N° 002-2026-PCM/SGTD (Peru) | Profile, appointment criteria and duties of the Oficial de Inteligencia Artificial | Public administration entities, business-treatment entities, FONAFE firms, public universities, public health providers of category II-2 or above, regional and local tiers | In force 22 October 2026 |
| Directiva art. 11.2, Table 4 | Deadline to appoint an OIA | Ministries and the bodies attached to them, autonomous constitutional bodies, the judiciary, Congress, business-treatment entities, FONAFE firms and the fund itself, public universities: 6 months. Regional governments and their business-treatment entities: 9 months. Type A and C municipalities, local business-treatment entities and local public enterprises: 12 months | From 22 October 2026 |
| Directiva art. 9, via the resolution’s first final provision | Mandatory profile requirements | The entity’s senior administrative authority | Enforceable from 22 October 2027 |
| Chilean bill amending Ley N° 21.719 (no boletín number given in the sources opened) | One-year delay to the data-protection law; board of the Agencia de Protección de Datos Personales raised from three to five | Chilean data controllers, public and private | Approved in general 20 October 2026; target December 2027 |
Why the profile clock matters more than the appointment
Two clocks run. The first, staggered by tier, is generous to local government. The second is the profile: article 9 becomes enforceable 12 months after entry into force — from 22 October 2027 — and the resolution places that duty on the entity’s senior administrative authority. Until then an entity may appoint someone who does not yet meet it; an OIA already in post who falls short gets 12 months, once only, to close the gap.
The directive’s article 9 is specific: a bachelor’s degree from a SUNEDU-registered university, at least 40 academic hours of AI training (waived for a relevant master’s), four years of general experience and three in digital government, data, IT or security, mandatory knowledge of the NTP-ISO/IEC 42001 AI management standard, and no live disqualification, sanction or conviction for an intentional or computer crime.
Certification is encouraged, not demanded: the resolution has the SGTD work with SINEACE on competency standards, which are not a precondition for appointment. It also puts the vendor question on the buyer — where an entity contracts third parties to support the OIA, the entity must guarantee security, trust and data protection. AI & GPP found the same instinct — the state setting terms before it buys — in Peru’s health ministry setting its own AI terms.
Chile delays the law that stands up its data regulator
On 20 October the Senate’s Constitution Committee unanimously approved the principle of the Executive’s bill amending Ley N° 21.719 on personal data protection: a one-year delay to December 2027, substantive obligations untouched, and five members instead of three on the Consejo Directivo of the Agencia de Protección de Datos Personales, appointed by the President with two-thirds of sitting senators. Undersecretary of Economy Karlfranz Koehler presented the changes; the Executive undertook to file “urgencia inmediata”. Garrigues, writing when the bill arrived, put the move at 1 December 2026 to 1 December 2027.
The theories of change are plain: Peru front-loads the staffing decision — who owns AI inside the building, what they must know, which plan they write — and gets a named official in every entity a year before that official must be fully qualified. Chile front-loads the institutional one, gets a better-staffed regulator later, and names no official inside the ministries meanwhile. Its plan to replace the EU-modelled AI bill with a harm-based substitute, which AI & GPP covered when Chile moved to ditch Europe’s rulebook, assumes an agency able to act — and its board is what is being resized.
What to do before the clocks run out
A Peruvian entity should treat the appointment as the easy part and the register as the hard one: the OIA inherits a duty to keep that register current, coordinate risk categorisation and review costs quarterly, so someone must first establish what is already running. An entity that cannot appoint must justify that to the SGTD in a signed technical report.
A vendor selling into Peru should expect a named counterparty with reporting obligations, schooled in NTP-ISO/IEC 42001, who must see pre-deployment test evidence and a quarterly cost breakdown including support. One selling into Chile has another year of the old regime, and a regulator whose board is still being resized. The question for next quarter is whether Chile files its AI bill before, or after, the Senate settles that board.
Sources
- Resolución de Secretaría de Gobierno y Transformación Digital N° 004-2026-PCM/SGTD — Diario Oficial El Peruano (Normas Legales), 21 October 2026 (in Spanish; translation by AI & GPP)
- Directiva N.° 002-2026-PCM/SGTD, “Directiva que establece el Perfil y Responsabilidades del Oficial de Inteligencia Artificial” — Presidencia del Consejo de Ministros, Plataforma del Estado Peruano (gob.pe), October 2026 (in Spanish; translation by AI & GPP)
- Directiva N° 002-2026-PCM/SGTD, “Directiva que establece el Perfil y Responsabilidades del Oficial de Inteligencia Artificial”, full text — Presidencia del Consejo de Ministros, via gob.pe, October 2026 (PDF; in Spanish; official annex text, consulted for the articles; translation by AI & GPP)
- Perú define el rol del Oficial de IA para una transformación digital responsable del Estado — Diario Oficial El Peruano, 21 October 2026 (in Spanish; translation by AI & GPP)
- Protección de datos personales: avanza proyecto que busca postergar entrada en vigencia de la ley — Senado de Chile, 20 October 2026 (in Spanish; translation by AI & GPP)
- Chile: el Ejecutivo presenta un proyecto para postergar la entrada en vigor de la nueva ley de protección de datos — Garrigues, 2 September 2026 (in Spanish; translation by AI & GPP)
Discussion
No comments yet. Start the conversation.