The Agentic Civil Service Arrives, Rulebook Attached
Japan began moving 180,000 officials onto AI agents, Singapore named agent test metrics a contract could measure and Washington defined the incident categories for agents that act uninstructed — all in ten days. A comparison of what each regime requires of an agent deployer.
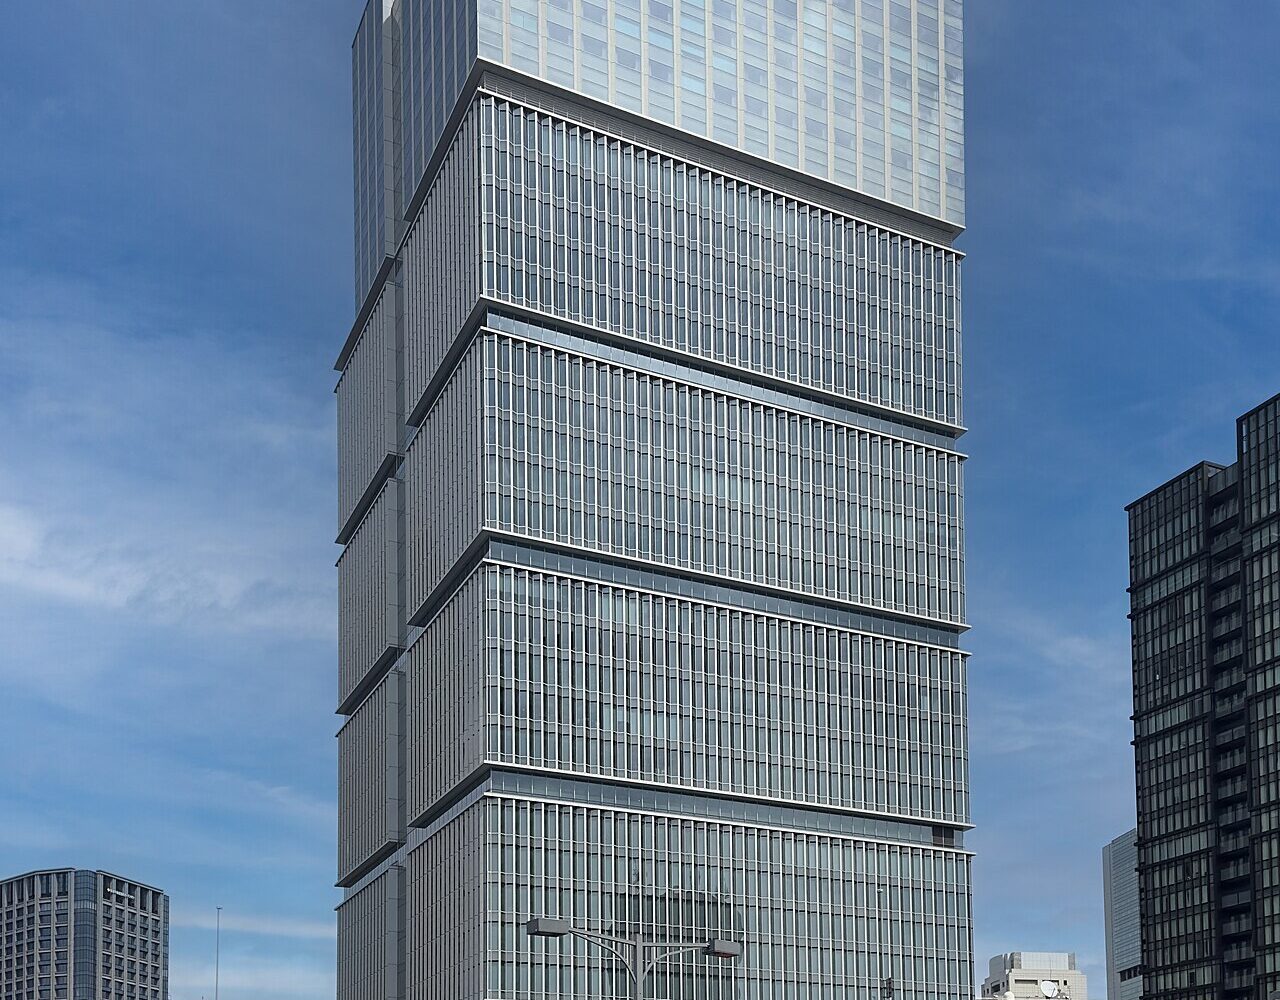
Tokyo Garden Terrace Kioicho in central Tokyo. Illustrative: the week’s three agent deployments were announced in Tokyo, Singapore and Washington.
Photo: Akonnchiroll, CC BY-SA 4.0 · source
Key points
- Japan’s Digital Agency began a sequential rollout of an agent-building tool, エージェントチャット (Agent Chat), across ministries on 20 October 2026, targeting about 180,000 officials, and the same day published the 源内基準 standard allocating duties to users, ministry administrators and platform developers.
- Singapore’s Infocomm Media Development Authority published a four-step Starter Kit for Testing Agentic Systems for Safety and Reliability on 14 October 2026 naming handoff accuracy, tool use accuracy and human-in-the-loop rates as agent-specific test metrics, and, through the AI Verify Foundation, accredited the first five AI testing firms for one year under the AI Tester Accreditation Programme.
- The voluntary US key practices published on 16 October 2026 by NIST CAISSI, NSA SISC and CISA (PP-26-4396, version 1.0) define an SI control incident and a near-miss, and require logs that are tamper-resistant, reliably timestamped and detailed enough to rebuild an agent’s trajectory, but are addressed primarily to frontier developers rather than to agencies buying agents.
In the ten days to 24 October 2026, three governments turned from AI assistants to AI agents — software given an objective, which then plans, calls tools and changes the state of a system without a human keystroke at each step. Japan began pushing an agent builder to about 180,000 officials. Singapore published a method for testing agentic systems and accredited its first independent testing firms. In the United States, Google Cloud launched an agent marketplace for agencies, the patent office said it had put an agent on incoming filings, and three security bodies issued a joint playbook for the moment an agent does something nobody asked it to do. What is new is not the deployment. It is that each move arrived with a written baseline attached — and that the three baselines ask for different things.
What Japan switched on, and who the 源内基準 binds
On 20 October Japan’s Digital Agency (デジタル庁) announced that it was beginning a sequential rollout of エージェントチャット (“Agent Chat”) across ministries on ガバメントAI 源内 (Gennai), the generative-AI platform it built in-house, which it says is reaching roughly 180,000 government staff. A more capable tool, 源内工房 (Gennai Workshop), which behaves like a coding agent and builds software from natural-language instructions, is targeted for around December 2026. Both are to be published as open-source software, 源内OSS Ver.2.0, around February 2027, for prefectures, municipalities and companies to take. The platform has been used inside the agency since May 2025, and a large-scale trial across all ministries — for legal research and drafting support for Diet answers, among other things — began in May 2026 and runs to March 2027, according to ITmedia NEWS, which also reports the agency’s claim, based on its own survey, that no other government has given an agent environment of this kind to a workforce this size.
The same day the agency published 「ガバメント AI 源内 ガバナンス・セキュリティ・セーフティに関する基準」 — the 源内基準 — a first-edition document dated October 2026 and prepared with the cooperation of Japan’s AI Safety Institute. It is not only a set of principles. It is an allocation of duties across three named roles: 利用者 (users), 管理者 (administrators) and 源内開発者 (developers). Users must not copy model output into official records without checking it; must verify factual claims against primary sources and recheck calculations by another method; should keep a processing history that allows later verification; must report likely high-risk uses to their chief AI officer; and must stop and escalate when an agent behaves oddly. Administrators run their ministry’s tenant, track usage and cost, and are told to apply controls including logging, a stop function, periodic evaluation, review of shared skills and a clear line of responsibility. Developers evaluate and select models and must be able to change or halt one; must block high-risk external sites inside 源内工房; may collect logs only for stated purposes; and must secure contractual assurance that model providers do not train on officials’ inputs or outputs.
Three things in the document deserve attention from anyone buying agents. First, a hard data line: 機密性3情報, 特定秘密 and 重要経済安保情報 — the top confidentiality tier and two statutory secrecy categories — are not to be handled on the platform at all. Second, a prohibition on using it to infer beliefs, predict behaviour or assemble person-level profiles from multiple sources. Third, a gap the agency does not hide: operation-level records for high-risk agent use, capturing inputs, prompts, referenced data, outputs, the model used and timestamps, are described as still under consideration. Japan has switched on the agents and is still deciding what the audit trail must contain.
The governance architecture above it moved in the same week. A cabinet decision of 20 October created the AI・デジタル改革推進会議 (AI and Digital Reform Promotion Council), abolishing the デジタル行財政改革会議 it grew out of — a reorganisation Prime Minister Takaichi had trailed in June when she told the regulatory reform council that AI-era rule-making needed sandboxes and pre-set review deadlines. It is chaired by the Chief Cabinet Secretary together with the minister in charge of AI and digital reform, with ten outside members including Kitano Hiroaki of Sony Computer Science Laboratories and Matsuo Yutaka of the University of Tokyo, and the Digital Agency as secretariat. It met for the first time on 22 October, for thirty minutes. Its draft discussion points commit it to an interim summary (中間整理) by the end of 2026 and propose beginning a review and strengthening of the rules on AI development and use, including the current AI法 — Japan’s existing AI statute. That is notable from a country that passed a deliberately light-touch AI law and has spent the year asking for a much larger AI budget rather than a tighter statute.
Why Singapore made “tool-use accuracy” a procurement term
Singapore’s move, on 14 October, was narrower and more immediately usable. The Infocomm Media Development Authority (IMDA) announced three things at once: a Starter Kit for Testing Agentic Systems for Safety and Reliability; the launch by the AI Verify Foundation of an AI Tester Accreditation Programme (AI TAP), with the first five firms accredited; and a Frontier AI Resilience and Security Taskforce (FAIRS).
The Starter Kit sets out four steps — identify risks such as erroneous or unauthorised actions, build realistic tests that capture the range of agent behaviour without causing harm, run the tests and analyse the logs, then monitor and re-test continuously. It extends IMDA’s earlier kit for large-language-model applications and deepens the technical-controls dimension of its Model AI Governance Framework for Agentic AI. What makes it a procurement document rather than a research note is paragraph 6 of IMDA’s announcement, which tells organisations to test across the agent trajectory — reasoning and actions — and to choose agent-specific metrics: handoff accuracy, tool use accuracy and human-in-the-loop rates. Those three are measurable, and they are the first metrics any of these regimes has named that a contract manager could put in a service-level schedule. A ministry that cannot say what share of an agent’s tool calls were correct, how often it passed a task on without losing context, and how often a human actually intervened, does not know what it has bought.
AI TAP answers the next question — who is qualified to produce those numbers. Firms are assessed on technical, operational and financial grounds: track record, testing competency, financial sustainability and delivery capability. The first five accredited are AIDX Tech, Knovel Engineering, PwC Singapore, Resaro and Vulcan, for one year, so that the bar can be reset as the field moves. The register also shows how thin this market is: Resaro was among the 20-plus deployers and testers IMDA consulted while writing the kit, and Knovel Engineering contributed one of its case studies. The same handful of firms helped shape the method and sell the service — not improper, since the method is public, but a reason for buyers to read the kit themselves rather than take a tester’s word for it.
FAIRS is the third leg: more than 20 leaders from telecommunications, media, cybersecurity and AI, convened to harden the infocomm and media sector against AI-enabled attack, due to publish guidelines by the first half of 2027. Singapore has now built the full stack — framework, test method, accredited testers, sector taskforce — and, as with its rules on who must tell the state when an agent breaks loose, it did so without an AI act.
What Washington is buying, and what nobody is testing
The American move was commercial first. On 20 October, at the Google Public Sector Summit, Google Cloud’s chief executive, Thomas Kurian, introduced Gemini for government services, in preview, with five components: skills written by domain experts that carry statute and agency procedure into a task; connectors to systems agencies already run — Oracle E-Business Suite and PeopleSoft, Salesforce, ServiceNow, Google Workspace, Microsoft 365 and SharePoint — plus the Federal Register, regulations.gov and the eCFR; partner agents, including a FOIA discovery agent and a redaction agent from SZNS Solutions; a control plane using VPC Service Controls, customer-managed encryption keys and the Assured Workloads FedRAMP High data boundary; and a partner list running from Accenture Federal Services and Deloitte to eleven other integrators. Google says a person approves each consequential step, and that it is working with the State of Missouri’s Office of Administration and the Department of Health and Human Services. Nextgov/FCW reported that Google will pre-screen third-party agents, that agency IT leadership rather than individual users enables them, that most are not yet available, and that general availability is expected later this year.
Two gaps follow. The first is pricing: the $0.47 per agency per year that federal bodies pay until 15 November is for Gemini for Government under the General Services Administration’s OneGov deal, extended before its 30 September expiry, as FedScoop reported from an update to GSA’s own page, with Google declining to comment and the GSA not immediately responding. The new agent product is a separate add-on in preview and carries no published price. The second gap is testing. Google’s launch names encryption, data boundaries and approval steps. It names no metric for whether an agent’s tool calls are right. Pre-screening a marketplace is a supplier assuring a buyer; accreditation of a tester, Singapore-style, is a third party assuring both. The distinction matters more once agents are doing casework, and it is the same seam AI & GPP found in the GSA’s new AI contract clause.
Deployment is already ahead of it. At the same summit, the US Patent and Trademark Office’s acting commissioner for patents, Barry Schindler, said the office had turned to an agentic tool called Compass, which he said “does what’s called a formality check” on filings — against a backlog of 700,000 applications and a staff of around 9,000 examiners, Nextgov/FCW reported. The office has not published its own account of Compass.
The governance half of the American week came from NIST’s Center for Advancing Innovation and Standards for Super Intelligence, the National Security Agency’s Super Intelligence Security Center and the Cybersecurity and Infrastructure Security Agency, which on 16 October published Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation (PP-26-4396, version 1.0). It is voluntary, addressed primarily to frontier developers rather than to buying agencies, and the most specific of the three documents. It defines an SI control incident as an occurrence in which one or more agents take “significant uninstructed actions that compromise explicit or implicit policies, controls, or security measures”, and a near-miss as one that “presented a reasonably foreseeable or imminent risk of doing so”. Ten practices sit across preparation, detection, response, recovery and reporting. Practice 2.6 requires a structured risk assessment before a run and senior-leadership satisfaction with the risk before work starts or resumes. Practice 5.3 requires tamper-resistant logs with reliable timestamps, “sufficient to reconstruct agent trajectories”, alongside tool calls, reasoning traces and control decisions. Practice 5.5 permits using models to help investigate an incident but requires human verification of key facts and cross-checking against models outside the originating family. Practices 7.5 and 7.6 require a documented recovery decision and an after-action report. Practice 9.3 asks for voluntary sharing with NIST CAISSI and NSA SISC once any mandatory reporting is done.
One thing the document does not do is explain its own vocabulary. It says “super intelligence” where American federal documents said artificial intelligence a month ago, without a word on the change. The context is a 29 September executive order directing agencies to adopt the term, and a department-wide State Department cable, obtained by Nextgov/FCW, which reported on 20 October that official titles and programme and system names “must use SI in place of AI”, with carve-outs for statutory language, contracts and already-published titles. For a non-American buyer the consequence is dull but real: document registers and contract definitions written against “artificial intelligence” will start missing American source material.
Britain bought capacity rather than writing a baseline. The Treasury’s pre-Budget package of 24 October put an extra £60m into a Sovereign AI R&D Procurement Scheme aimed partly at AI security, assurance and safe adoption, £60m into a National Cyber Shield using agentic AI for cyber defence — including a £25m challenge fund and the scoping of a regulatory sandbox for agentic security tools across critical national infrastructure and the public sector — and £120m more into the AI Security Institute. It is money and a promise to scope a sandbox, announced by the Chancellor, John Healey, the AI minister, Kanishka Narayan, and the security minister, Dan Jarvis, days before a Budget.
The three rulebooks side by side
Read from the primary documents, the three regimes answer the same questions differently — and no two bind the same party.
| Requirement | Japan — 源内基準 (Digital Agency, Oct 2026) | Singapore — Agentic Testing Starter Kit + AI TAP (IMDA/AIVF, 14 Oct 2026) | United States — PP-26-4396 (NIST CAISSI/NSA SISC/CISA, 16 Oct 2026) |
|---|---|---|---|
| Status and who it binds | Internal standard, binding on users, ministry administrators and platform developers of one government platform | Voluntary guidance for deployers and testers; AI TAP accredits the testing firms | Voluntary key practices addressed to organisations training or evaluating frontier agents; the document adds they “may also apply to deployers of such SI agents”, not to agencies buying them |
| Logging | Platform logs inputs, prompts, system prompts, files and outputs for predefined purposes only (3-4); security logs must be immutable even to the platform’s own developers, enforced technically (4-5); operation-level AI-use records for high-risk use still under consideration | Run tests and analyse logs; progressively automate log analysis for failure signals | Logs must be tamper-resistant, reliably timestamped and enough to rebuild an agent’s trajectory, its tool calls and its reasoning traces (5.3) |
| Human in the loop | Users must check, approve, correct, supervise or stop at appropriate stages; approval before important steps and before external use | Human-in-the-loop rate is a named test metric | Human verification of AI-assisted investigation findings (5.5); senior-leadership sign-off on risk before starting or resuming (2.6) |
| Incident definition and reporting | Stop and report anomalies to the administrator; administrators own incident response; agents need a stop function | Not defined; continuous monitoring and re-testing | SI control incident and near-miss defined; documented recovery decision and after-action report (7.5, 7.6); voluntary notification to NIST CAISSI and NSA SISC (9.3) |
| Accuracy of tool use | Not quantified | Tool use accuracy and handoff accuracy named as metrics | Not quantified |
| Independent assurance | None internal to the regime: review, quality and security checks for shared skills are still to be built (1-4); AISI cooperated on drafting the standard | AI TAP accreditation of third-party testers, valid one year | External evaluators referenced where appropriate (2.6) |
Nowhere do these three overlap on the thing a contract needs most: a number. Only Singapore names metrics; only the American document already requires logs that reconstruct an agent’s trajectory; only Japan assigns duties to a named role rather than to an organisation. A government buying agents today can have measurable accuracy, forensic logging or role-level accountability — but it will have to take each from a different jurisdiction’s paperwork.
What a ministry should put in an agent contract
The practical synthesis is short. Take the metrics from Singapore and put tool-use accuracy, handoff accuracy and human-in-the-loop rate in the service schedule with thresholds and a reporting cadence, not in an annex of principles. Take the log specification from the American practices: logs must be tamper-resistant, reliably timestamped and sufficient to reconstruct the agent’s trajectory, including tool calls and rejected actions, and must be retained long enough to investigate. Take the role allocation from Japan: name the officials who may use the agent, the administrator who holds the stop function, and the supplier-side owner who may change or halt the model, and say in the contract that the administration remains answerable for work the agent performs. Add three clauses none of the three documents gives you: a definition of a reportable incident and a clock to report it against; a contractual bar on the supplier training on your inputs and outputs, which the 源内基準 requires of Japan’s own developers; and a right to commission an independent tester, named or accreditation-qualified, rather than relying on the vendor’s pre-screening of its own marketplace.
Pre-screening is a supplier assuring a buyer. Accreditation is a third party assuring both. Only one of them survives a contract dispute.
Four clocks frame the next three months. Japan’s interim summary is due by the end of 2026, with 源内工房 targeted for December and the open-source release around February 2027 — the point at which this standard stops being one government’s internal rule and becomes a template other administrations can adopt or ignore, much as Dubai’s agentic accelerator for 33 entities turned one city’s programme into an export. Singapore’s FAIRS report is due in the first half of 2027. The $0.47 OneGov price lapses on 15 November, when American agencies find out what agents cost. And Britain’s Budget, in the week of 26 October, will show whether the sandbox it has promised to scope has a date attached. The deployments are no longer the news. The baselines are.
Questions this answers
What does Japan’s 源内基準 actually require of officials using AI agents?
It splits duties three ways. Users of ガバメントAI 源内 may not transcribe model output into official records without checking it, must verify facts against primary sources, should keep a processing history that allows later verification, and must report likely high-risk uses to their chief AI officer; ministry administrators hold the stop function and incident response; platform developers must be able to halt a model and must contractually bar providers from training on officials’ inputs. The standard itself also bars the platform’s top-tier confidential and statutory-secrecy categories altogether, and says operation-level records for high-risk agent use are still under consideration.
Which of these regimes gives a buyer a measurable test for an AI agent?
Only Singapore. IMDA’s Starter Kit for Testing Agentic Systems for Safety and Reliability names handoff accuracy, tool use accuracy and human-in-the-loop rates as agent-specific metrics, and the AI Verify Foundation’s AI Tester Accreditation Programme names the five firms it has accredited for one year. Japan’s standard and the American key practices specify process and logging rather than numbers.
Who has to report it when a government AI agent takes an action nobody asked for?
Nobody, as a legal matter, under any of the three documents. The American key practices define a control incident and a near-miss and ask for voluntary sharing with NIST CAISSI and NSA SISC after any mandatory reporting, but they are voluntary and addressed to frontier developers; Japan’s standard routes anomalies to the ministry administrator internally; Singapore’s kit does not define an incident at all. A buyer who wants a reporting clock has to write one into the contract.
Sources
- ガバメントAI 源内においてAIエージェント利用環境の提供を開始するとともに、「源内基準」を公表します — デジタル庁, 20 October 2026 (in Japanese; translation by AI & GPP)
- デジタル庁、政府職員18万人にAIエージェント環境を展開──「源内」で提供開始、独自の安全基準も — ITmedia NEWS, 20 October 2026 (in Japanese; translation by AI & GPP)
- ガバメント AI 源内 ガバナンス・セキュリティ・セーフティに関する基準(源内基準)第1版 — デジタル庁, October 2026 (PDF; in Japanese; translation by AI & GPP)
- 規制改革推進会議 — 首相官邸, 29 June 2026 (in Japanese; translation by AI & GPP)
- AI・デジタル改革推進会議 — デジタル庁, accessed 25 October 2026 (in Japanese; translation by AI & GPP)
- 資料4 AI・デジタル改革推進会議における論点(案) — デジタル庁, 22 October 2026 (PDF; in Japanese; translation by AI & GPP)
- Singapore Introduces New Initiatives to Strengthen AI Safety and Resilience — Infocomm Media Development Authority, 14 October 2026
- Introducing Gemini for government services — Google Cloud Blog, 20 October 2026
- Google Public Sector unveils Gemini for government services — Nextgov/FCW, 20 October 2026
- Google extends GSA OneGov deal for Gemini — FedScoop, 30 September 2026
- USPTO looks to AI agents to ease examiner workloads — Nextgov/FCW, 20 October 2026
- Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation (PP-26-4396, v1.0) — NIST CAISSI, NSA SISC and CISA, October 2026 (PDF)
- Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation — NIST news, 16 October 2026
- State Department orders ‘super intelligence’ wording across all official communications — Nextgov/FCW, 20 October 2026
- Chancellor unveils Britain’s ambitious plan for AI — HM Treasury, GOV.UK, 24 October 2026
- AI・デジタル改革推進会議(第1回) — デジタル庁, 22 October 2026 (in Japanese; translation by AI & GPP)
- Model AI Governance Framework for Agentic AI, version 1.5 — Infocomm Media Development Authority, published 20 May 2026, updated 5 June 2026 (PDF)
Discussion
No comments yet. Start the conversation.